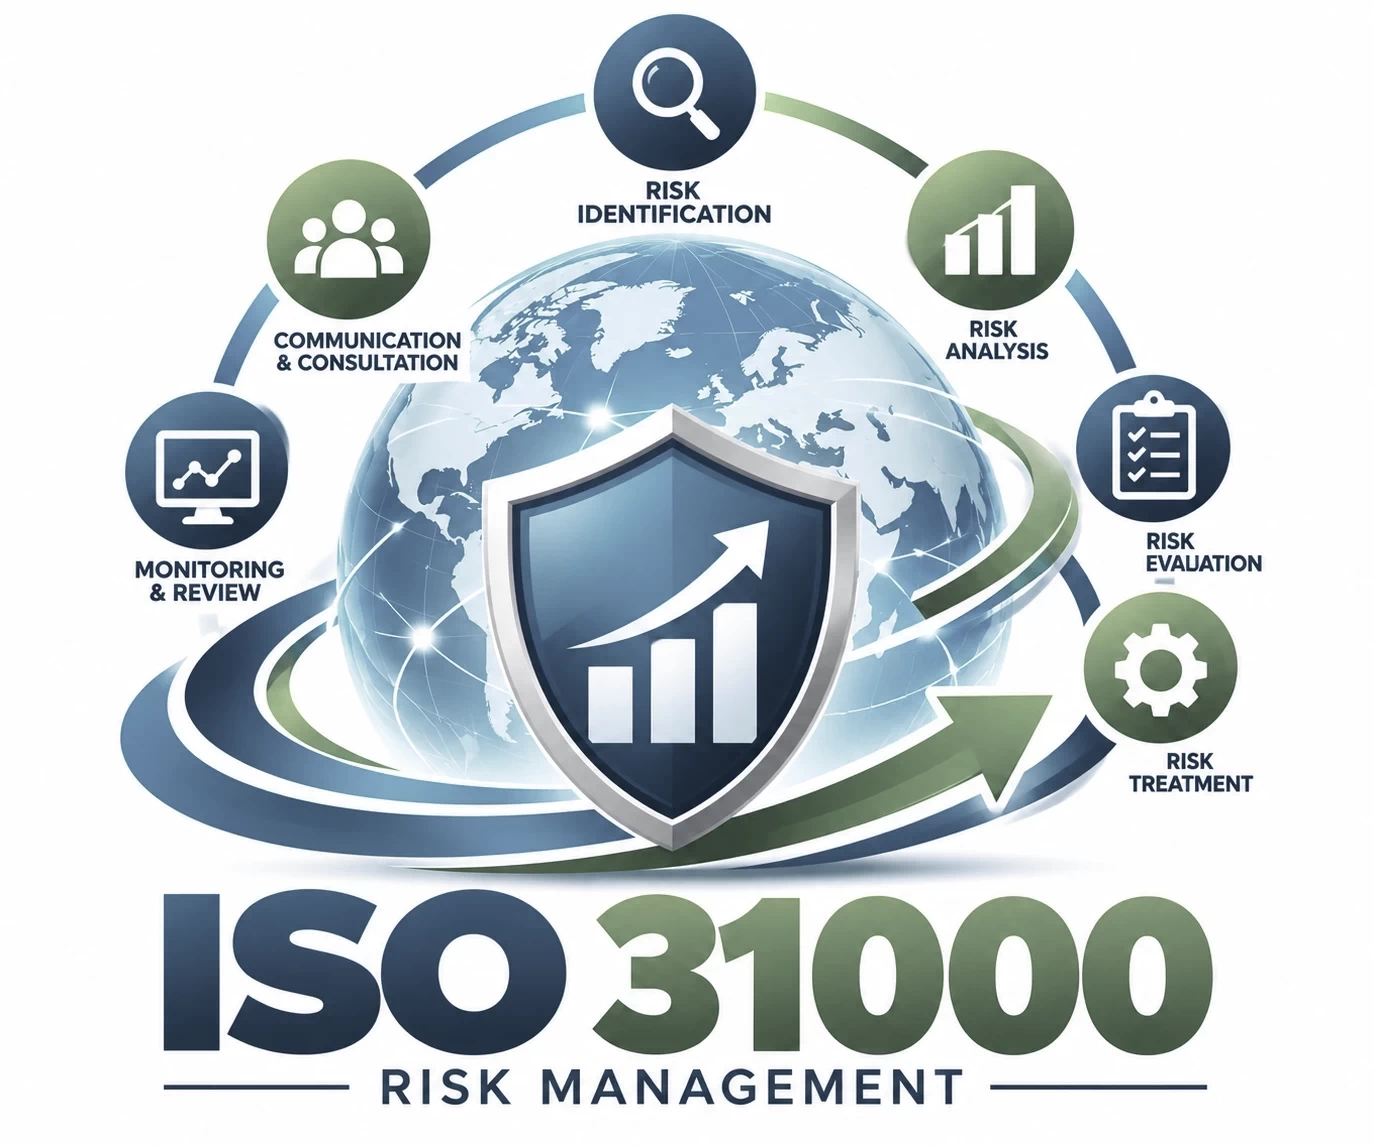
ISO 31000:2018 provides principles, an overarching framework, and a systematic process for managing risk across all organizational functions. Rather than viewing risk solely as a threat to be avoided, ISO 31000 defines risk as the "effect of uncertainty on objectives", empowering leadership to identify threats, capitalize on opportunities, and safeguard corporate value.
As business landscapes face volatile supply chains, cybersecurity vulnerabilities, regulatory tightening, and geopolitical shifts, modern enterprises cannot rely on siloed risk assessments. ISO 31000 embeds risk governance directly into corporate decision-making, strategic planning, and operational workflows.
At SriWin, we help organizations design customized Enterprise Risk Management (ERM) architectures. From defining board-level risk appetite and tolerance to deploying practical assessment techniques (ISO 31010), our consulting and masterclasses ensure your organization remains resilient, agile, and prepared for future disruptions.
Embedding risk management into organizational purpose, strategic planning, budgeting, and performance management at the board level.
Establishing qualitative and quantitative risk thresholds to clarify acceptable exposure levels across strategic and financial operations.
Deploying identification, analysis, and evaluation methods using ISO/IEC 31010 techniques (Bow-tie analysis, HAZOP, SWIFT, and Delphi).
Developing mitigation, transfer, acceptance, or avoidance strategies to optimize risk-reward trade-offs and bolster operational controls.
Designing dynamic Key Risk Indicators (KRIs), corporate risk dashboards, and early warning systems to detect emerging risks in real time.
Facilitating transparent communication channels between executive leadership, operational managers, regulators, and external stakeholders.
Provide leadership with objective, data-backed risk intelligence to pursue high-return business opportunities safely.
Protect business continuity, financial solvency, and brand reputation by heading off catastrophic disruptions.
Unify operational, financial, cyber, environmental, and reputational risk assessments under a single coherent framework.
Satisfy institutional investors, rating agencies, lenders, and regulatory authorities with audit-ready compliance evidence.
Direct contingency budgets and risk reduction resources where they mitigate the highest exposure points.
Accelerate organizational recovery times and responsiveness when unforeseen external shocks or market shifts occur.
Collaborate with SriWin’s experienced risk advisory specialists to design an ISO 31000 compliant risk architecture tailored to your business strategy.
Request Risk Management Consultation