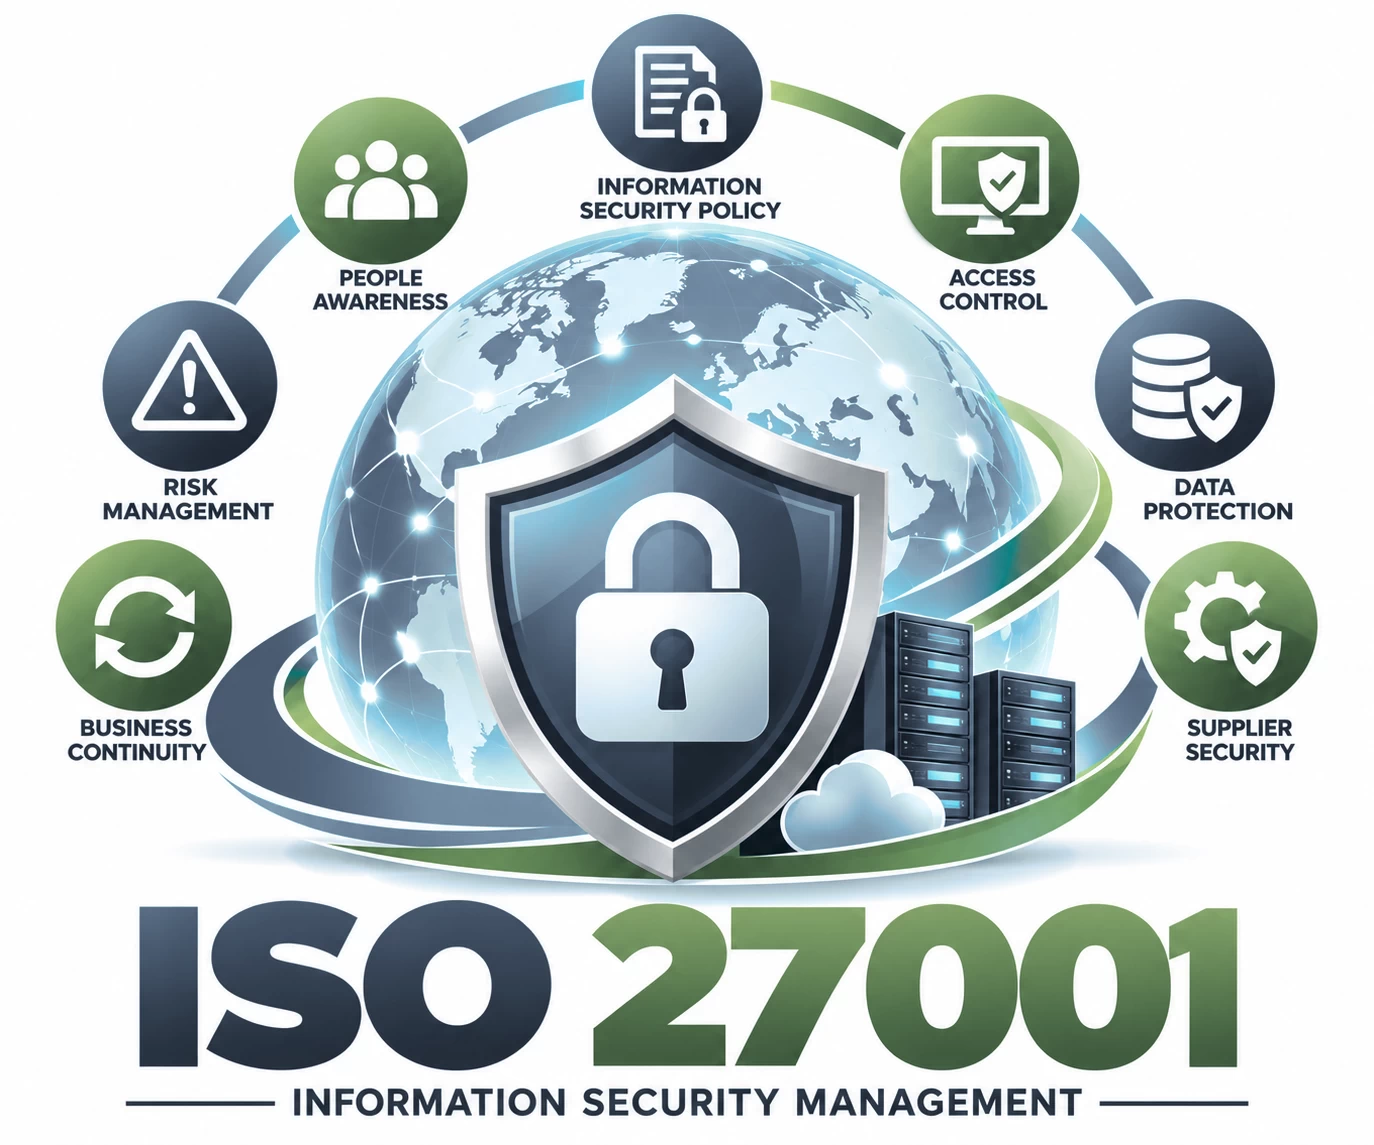
ISO/IEC 27001:2022 is the internationally recognized benchmark standard for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). It provides organizations with a risk-managed framework to secure confidential data across people, processes, and technology.
The updated 2022 revision reorganizes information security controls into four focused themes (Organizational, People, Physical, and Technological) and introduces critical modern controls covering threat intelligence, cloud services security, data leakage prevention (DLP), web filtering, and secure coding.
At SriWin, we guide enterprises through end-to-end ISMS rollouts—from conducting comprehensive information security risk assessments and designing the Statement of Applicability (SoA) to aligning with statutory data privacy laws (DPDPA, GDPR, HIPAA) and preparing your in-house internal audit cadre for stage-1 and stage-2 accreditation audits.
Systematic threat and vulnerability modeling across informational and hardware assets to calculate impact and likelihood.
Structured justification and operational mapping for the 93 Annex A security controls categorized under the 2022 revision.
Implementation of modern 2022 controls: cloud services governance, sensitive data classification, data masking, and leak prevention.
Role-based access policies (RBAC), multi-factor authentication (MFA), password management, and cryptographic key lifecycles.
Protocols for identifying, containing, and reporting data breaches alongside disaster recovery (DR) and business continuity plans.
Assessing external vendor risks, supply chain cybersecurity agreements, and SLA compliance monitoring.
Provide tangible proof to global clients and tech partners that proprietary data and intellectual property are protected.
Ensure seamless compliance with India's Digital Personal Data Protection Act (DPDPA), EU GDPR, IT Act 2000, and international data laws.
Significantly lower the likelihood of ransomware attacks, unauthorized system breaches, phishing traps, and data leaks.
Fulfill mandatory pre-qualification criteria for international software contracts, government RFPs, and corporate tech deals.
Avoid devastating financial penalties, negative headlines, litigation, and brand erosion resulting from public security incidents.
Ensure mission-critical systems and server infrastructures maintain high availability and rapid disaster recovery capabilities.
Collaborate with SriWin’s certified information security lead auditors to design a resilient, audit-ready ISMS framework tailored to your technology ecosystem.
Request ISO 27001 Proposal